
n8n human in the loop: approvals that survive retries
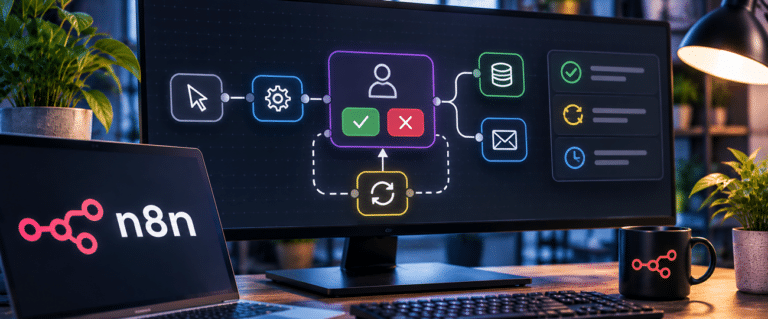
An n8n human-in-the-loop approval should authorise one specific action, not simply release a paused workflow. If a reviewer clicks twice, a worker retries, or an AI Agent changes the proposed amount, the workflow must not quietly perform a second or different action.
This guide builds that boundary around a reusable, importable mock workflow. It covers approval, rejection, expiry, duplicate requests, changed payloads and retries using PostgreSQL as durable state. The accompanying files are a demonstration to validate locally, not a claim of a completed live test or a production-ready authorisation system.
Import the workflow and run a safe approval exercise
Example configuration: three POST webhooks for proposing, deciding and performing an action; a PostgreSQL approval record; a unique mock-effect table; an audit-event table; and a five-minute expiry sweep. No Gmail message, refund or third-party API call is made. The only approved effect is a database insert.
- Use an isolated n8n instance and a disposable PostgreSQL database. Apply
01-schema.sqlto create the tables and functions. - Import
n8n-human-in-the-loop-mock.jsonthrough n8n’s workflow import option. Assign a PostgreSQL credential to all four Postgres nodes. - Keep the webhooks private. The fixture intentionally has no webhook authentication, so do not expose it to the public internet.
- Publish the workflow on the isolated instance and run
02-smoke-test.ps1against its local/webhook/hitl-demobase URL. - Inspect
hitl_demo.approvals,hitl_demo.mock_effectsandhitl_demo.audit_events. Verify there is no more than one mock-effect row for each approval ID.
The companion package contains the workflow JSON, SQL setup, PowerShell test and a README. Its tests define the expected outcomes; you still need to run them on your own n8n version and database before the example can be treated as verified.
Keep the approval state outside the waiting execution.
The simplest n8n pattern is to send a message and wait for a response. That is fine for low-risk, single-run decisions. n8n also supports human review of selected AI Agent tool calls, as explained in its human-in-the-loop tool-call documentation. The harder operational requirement is preserving one decision across duplicate incoming events, restarted runs and multiple workers.
For that, it approves its own record. The demonstration stores an approval_id, integer action version, immutable proposed JSON action, deadline, current status and decision metadata. The ID must come from a stable business operation, such as a particular quotation revision. An n8n execution ID alone is not necessarily stable when an upstream event is delivered again.
The permitted lifecycle is deliberately narrow: pending becomes approved, rejected or expired. An approved request can become executed or expire before execution. Rejection and expiry are terminal. If the author changes the proposal, create a new approval ID or revision rather than overwriting the old record.
This separation also makes recovery less ambiguous. After a restart, a fresh execution can ask the database what happened instead of assuming the previous workflow reached its final node. Execution history remains useful for debugging, but should not be the sole record of an authorisation decision.
Freeze the exact action before the reviewer sees it
Imagine an AI Agent proposing a quotation to mock@example.invalid for £125. A reviewer should see the actual recipient, amount, currency, action type and version. Showing only a summary such as “send the quotation” creates an obvious gap: the action might be rebuilt with different parameters when the workflow resumes.
{
  "approval_id": "quote-104-v1",
  "version": 1,
  "action": {
    "kind": "send_quotation",
    "recipient": "mock@example.invalid",
    "amount_gbp": 125,
    "currency": "GBP"
  },
  "ttl_seconds": 900
}
Submit that object to POST /webhook/hitl-demo/propose. The database stores the original action as JSONB. At the decision endpoint, it compares the submitted version and action against the saved record. At the mock execution endpoint, it performs the comparison again.
Change amount_gbp from 125 to 999 after approval, and the expected response is payload_mismatch. The original approval is not silently transferred to the higher amount. The stored action can still be performed if it has not expired; the amended action needs a new approval. JSONB equality is suitable for this structured demo because object key order is irrelevant. A production design that requires byte-for-byte approval evidence should also persist a canonical payload digest and the exact reviewed representation.
Handle repeated clicks and retries at the database boundary
There are two separate duplicate problems. A reviewer may click Approve twice, and a worker may attempt the approved action twice. Deduplicating notification messages solves neither reliably.
The decision function locks the approval row before changing its status. Only a pending record can become approved or rejected. A repeated approval receives already_approved rather than issuing another authorisation. The proposal endpoint similarly detects an identical retried request, while rejecting a different payload that reuses the same approval ID.
Execution has a separate guard. The mock-effect table uses the approval ID as its primary key, and the execution function checks status, deadline, version and saved payload under a row lock. Once a matching effect is written, the status becomes executed. A retry receives already_executed, with no second mock insert.
Do not mistake this for exactly-once delivery to Stripe, Gmail or another external API. A database commit cannot atomically include an unrelated network request. For real actions, create a transactional outbox entry, dispatch it with a stable provider idempotency key where supported, record the provider’s receipt and reconcile uncertain timeouts before retrying. If the destination offers no idempotency support, manual reconciliation may be safer than automatic repetition.
Expire unanswered requests without treating silence as consent
The sample’s deadline starts at proposal creation. It is checked when a reviewer responds and again before the mock effect. If an approval expires while the workflow is idle, a late click cannot revive it. A scheduled sweep also marks overdue pending or approved records as expired, giving operators a useful queue status even when nobody clicks.
There is a trade-off here: the fixture uses one deadline for both the review and execution stages. That is conservative, but a busy approval queue may need separate review_expires_at and execution_expires_at fields. Otherwise, a valid decision made seconds before expiry might not leave time to execute. Define those windows explicitly rather than quietly extending an old approval.
For urgent or high-value actions, timeout should mean deny or re-review, not automatic approval. A reminder or escalation can start a new review process, but must not change the meaning of the expired decision.
Run failure cases, not just the happy path.
The PowerShell smoke test exercises the following cases with mock data. These are expected results to verify after import, not reported findings from a live test.
| Test | Expected outcome | What to inspect |
|---|---|---|
| First proposal | created | One pending approval record |
| Same proposal delivered twice | duplicate_request | No replacement of the original payload or deadline |
| Different payload reuses its ID | proposal_conflict | Original proposal remains unchanged |
| Approve, then click again | approved, then already_approved | One decision transition |
| Change the amount after approval | payload_mismatch | No mock effect for the altered amount |
| Execute, then retry | mock_written, then already_executed | Exactly one mock-effect row |
| Reject or approve after expiry | rejected or expired | No effect row for either case |
Also run two perform requests concurrently after approval, restart n8n between decision and performance, and inspect the final database rows. Those additional recovery checks need a live environment; the sequential smoke test does not cover them. A red test should block replacing the mock insert with a real action.
See more of our reporting in Google Top Stories, AI Overviews and AI Mode.
Authentication and evidence are separate from an approval click
The demo accepts a caller-supplied reviewer_id purely to illustrate state transitions. It is not identity verification. A forwarded approval link or an arbitrary webhook body must not be trusted to identify an authorised reviewer. Before production, require authenticated access, resolve reviewer identity from the authenticated session or gateway, check role and action-specific permissions, and reject stale or replayed tokens.
Keep two records when a live service is involved: an approval record proving which action was authorised, and an execution receipt showing what the provider accepted. The fixture’s audit table records transitions and attempted payload mismatches, but does not prove that an external provider completed anything. Error responses, reconciliation outcomes, manual overrides and any redacted personal data need their own retention policy.
Use the smallest approval system that matches the risk.
For a simple internal reminder or low-risk draft, n8n’s native review nodes may be enough. For a refund, public publication or bank-detail change, an approval record plus durable execution claim earns its extra database work. If several workflows share the same reviewers and rules, move the approval policy into a reusable service rather than copying a fragile Wait-node branch everywhere.
A spreadsheet queue can be reasonable when the actual approved action is performed manually. Our comparison of Excel and Google Sheets automation tools covers that lighter approach. It becomes unsuitable once multiple automated workers need atomic claims, enforced deadlines and a reliable audit trail.
Before replacing the mock insert with a real action
- Authenticate proposal and decision endpoints and verify the approver’s permission for the action.
- Store and display the same immutable action version; require a new approval after edits.
- Use a stable operation ID across source retries, not a newly generated ID on every run.
- Lock state transitions and enforce uniqueness in persistent storage.
- Handle approval expiry and execution expiry explicitly, including restart recovery.
- Introduce an outbox, destination idempotency and provider receipts before real side effects.
- Check duplicate clicks, parallel requests, rejection, stale payloads and expired approval in a disposable environment.
The safe promotion criterion is specific: a rejected, expired or changed proposal must create no effect, while repeated delivery of the same approved proposal must create at most one. Until the integration tests and authentication checks pass on your own deployment, keep the workflow mocked.
You Might Also Like:
Best AI Coding Tools 2026
Claude Code Pricing 2026
Claude Code Best Practices
